Let us understand how we can help you
INDSAFE provides functional safety services to help organizations assess, design, implement, and verify safety-related instrumented systems used to reduce process risk.
Our functional safety services cover Safety Integrity Level (SIL) assessment and verification, Layers of Protection Analysis (LOPA), Safety Instrumented System (SIS) evaluation, Safety Instrumented Function (SIF) assessment, and functional safety lifecycle support.
We apply risk-based engineering principles and relevant functional safety standards to help organizations establish appropriate safety requirements, evaluate protection layers, and verify that safety instrumented functions can achieve the required level of risk reduction.
What is Functional Safety?
Functional safety is the part of overall safety that depends on systems, equipment, and controls operating correctly in response to defined hazardous conditions or failures.
In process and manufacturing industries, hazardous scenarios may arise from abnormal process conditions such as high pressure, high temperature, excessive flow, low level, or loss of containment. Instrumented protection systems can detect these conditions and initiate predefined actions to move the process toward a safe state.
Functional safety therefore focuses on questions such as:
- What hazardous scenarios require instrumented protection?
- What safety functions are required?
- How much risk reduction does each safety function need to provide?
- What Safety Integrity Level (SIL) is required?
- Can the Safety Instrumented Function (SIF) achieve its required SIL?
- Are the sensors, logic solver, and final elements sufficiently reliable?
- How should the safety system be maintained throughout its lifecycle?
Functional safety is not limited to the selection of a safety instrumented system. It involves a lifecycle of hazard analysis, specification, design, implementation, verification, operation, maintenance, testing, and eventual modification or decommissioning.
Understanding SIF, SIS and SIL
Three terms are central to functional safety: Safety Instrumented Function (SIF), Safety Instrumented System (SIS), and Safety Integrity Level (SIL).
Safety Instrumented Function (SIF)
A SIF is a specific safety function designed to detect a hazardous condition and take a defined action to reduce risk.
A typical SIF consists of:
- Sensors that detect the process condition
- Logic solver that processes the input and initiates the safety action
- Final elements such as valves or other actuators that bring the process toward a safe state
For example, a high-pressure condition may initiate a shutdown function that isolates a process section or stops feed to prevent escalation.

Safety Instrumented System (SIS)
An SIS is the system used to implement one or more SIFs.
The SIS generally includes the sensors, logic solver, final elements, associated interfaces, and supporting arrangements required for the safety functions.
The reliability of the complete SIF depends on the performance of its individual components and the way the system is designed, tested, maintained, and operated.
Safety Integrity Level (SIL)
SIL is a measure of the required integrity of a safety function.
For low-demand safety functions, SIL is associated with the average probability of failure on demand (PFDavg). Higher SIL requirements correspond to greater required risk reduction and lower allowable probability of dangerous failure on demand.
SIL assessment therefore helps determine the performance requirement for an applicable safety function; it does not simply assign a SIL to an entire plant or process.
SIL Levels & Risk Reduction

Functional safety standards define four SIL levels, from SIL 1 to SIL 4, with progressively higher integrity requirements.
For process-industry applications, SIL determination commonly focuses on the amount of risk reduction required from a particular safety instrumented function.
A SIL assessment may therefore consider:
- Initiating event frequency
- Consequence severity
- Existing independent protection layers
- Required risk reduction
- Target SIL for the SIF
- Applicable operating mode
- Demand frequency
- Reliability of SIF components
The required SIL should be established through an appropriate risk assessment rather than being selected simply because a system is considered “safety critical.”
Our Functional Safety Services
INDSAFE provides functional safety services covering different stages of the functional safety lifecycle.
1. SIL Assessment
SIL assessment determines the required integrity level for applicable safety instrumented functions based on the risk associated with the hazardous scenario.
Depending on the project methodology, SIL determination may use techniques such as LOPA or other appropriate risk assessment methods.
The assessment considers the initiating event, consequences, existing protection layers, and required additional risk reduction.
2. SIL Verification
SIL verification evaluates whether the designed SIF can achieve the required SIL based on factors such as:
- Hardware architecture
- Failure rates
- Safe and dangerous failure modes
- Diagnostic coverage
- Common cause considerations
- Proof-test intervals
- Proof-test coverage
- Component reliability
- Hardware fault tolerance
- PFDavg calculations
The objective is to verify that the implemented or proposed SIF architecture meets the required performance target under the defined assumptions.
3. LOPA Studies
Layers of Protection Analysis (LOPA) is a structured semi-quantitative technique used to evaluate accident scenarios and the effectiveness of independent protection layers.
A LOPA study can consider:
- Initiating event frequency
- Consequence severity
- Independent protection layers
- Enabling conditions
- Conditional modifiers where applicable
- Existing risk reduction
- Additional risk reduction requirements
Where a Safety Instrumented Function is identified as a required independent protection layer, the LOPA outcome can support determination of the required SIL.
Learn more about our HAZOP Study Services and QRA Services.
4. SIS Evaluation
SIS evaluation examines the architecture and performance of safety instrumented systems against defined functional and integrity requirements.
The assessment may include:
- SIF architecture
- Sensors and transmitters
- Logic solver
- Final control elements
- Voting arrangements
- Diagnostics
- Failure modes
- Testing requirements
- Bypass and override considerations
- Maintenance and proof-testing arrangements
5. SIF Assessment
A Safety Instrumented Function is evaluated as a complete safety function rather than as an isolated instrument or component.
Our assessment considers the complete signal path from:
Sensor → Logic Solver → Final Element
This helps identify whether the complete SIF can achieve its required safety performance.
6. Functional Safety Lifecycle Support
Functional safety requires management throughout the lifecycle of a safety instrumented system.
Support may include activities associated with:
- Hazard and risk assessment
- Safety requirements
- SIF identification
- SIL determination
- Safety requirements specification
- SIS design review
- SIL verification
- Installation and commissioning considerations
- Proof testing
- Operation and maintenance
- Management of modifications
- Functional safety performance review
The exact scope depends on the project phase, facility, applicable standards, and client requirements.
How LOPA Supports Functional Safety

LOPA is often used when a structured, semi-quantitative evaluation of a specific hazardous scenario is required.
A simplified LOPA assessment can be represented as:
Initiating Event → Consequence → Existing Independent Protection Layers → Residual Risk → Additional Risk Reduction Requirement
For example, a hazardous scenario may have an initiating event followed by a process deviation. Existing protection layers may reduce the likelihood of the consequence, but the remaining risk may still require additional protection.
Where the additional protection is assigned to a SIF, the required risk reduction can support the determination of the target SIL.
LOPA therefore provides an important connection between process hazard analysis and functional safety, while the detailed SIL verification subsequently evaluates whether the SIF design can achieve the required integrity.
Functional Safety and HAZOP
HAZOP and functional safety address related but different questions.
A HAZOP study systematically examines process deviations, their causes, consequences, safeguards, and recommendations.
Functional safety analysis focuses on the safety functions required to reduce risk and whether those functions achieve the required integrity.
HAZOP findings can therefore provide important inputs to functional safety activities, including identification of hazardous scenarios and existing safeguards.
However, not every HAZOP recommendation becomes a SIF, and not every HAZOP scenario requires SIL assessment.
Learn more about our HAZOP Study Services.
Functional Safety and QRA
Quantitative Risk Assessment (QRA) and functional safety studies have different purposes.
QRA can quantitatively characterize risk using event frequencies, consequence modelling, and risk metrics such as individual risk and societal risk.
Functional safety studies focus on the performance and integrity of safety-related instrumented functions.
Depending on the project, QRA may provide supporting risk information, while functional safety activities address specific instrumented protection requirements.
Learn more about our QRA Services.
Our Functional Safety Approach
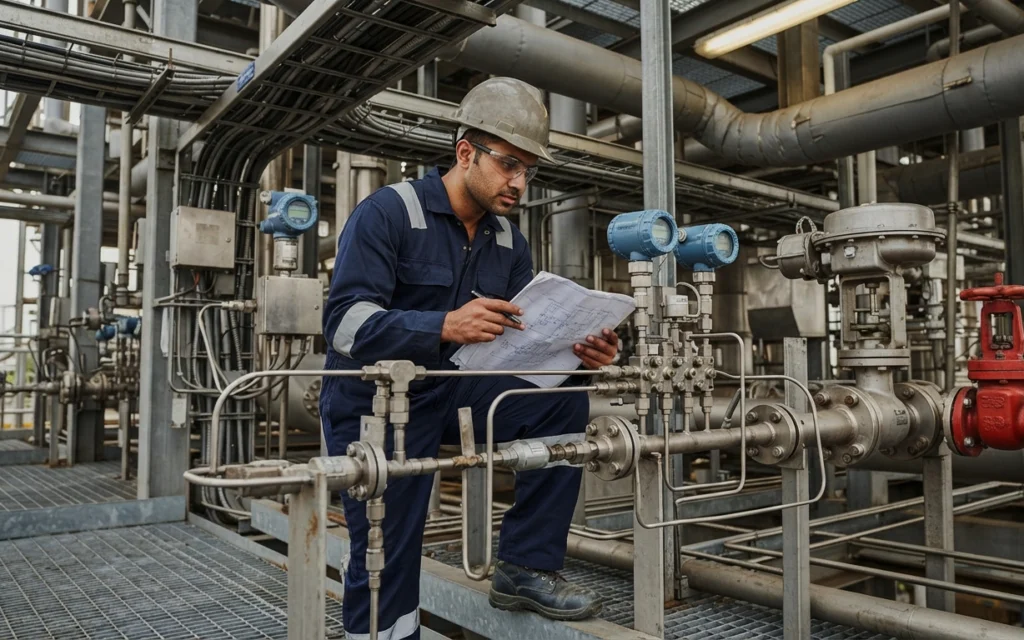
Our approach is structured around the requirements of the project and the applicable functional safety lifecycle.
Step 1: Understand the Process and Scope
We review available process, instrumentation, design, operating, and safety information to understand the facility and the scope of the assessment.
Step 2: Identify Hazardous Scenarios
Relevant hazard scenarios and process deviations are reviewed using appropriate process safety studies and available project information.
Step 3: Identify Safety Functions
Required safety functions are identified based on the hazardous scenarios, existing safeguards, and risk reduction requirements.
Step 4: Determine Required SIL
Where a SIF is required, an appropriate SIL determination methodology is applied to establish the required integrity level.
Step 5: Evaluate the SIS/SIF Design
The proposed or existing SIF architecture is evaluated to determine whether it can achieve the required performance.
Step 6: Perform SIL Verification
Where applicable, reliability calculations and architectural considerations are used to verify the achieved SIL against the target requirement.
Step 7: Develop Recommendations
Findings, assumptions, limitations, and recommendations are documented to support practical implementation and lifecycle management.
Typical Information Required
Depending on the scope, functional safety studies may require information such as:
- Process Flow Diagrams (PFDs)
- Piping and Instrumentation Diagrams (P&IDs)
- Process descriptions
- Cause and Effect diagrams
- Control narratives
- Instrument index
- Shutdown philosophy
- Alarm and trip information
- HAZOP/HAZID study reports
- LOPA worksheets, where available
- SIF list
- SIS architecture
- Instrument datasheets
- Failure-rate data
- Proof-test information
- Voting architecture
- Logic solver information
- Final element information
- Operating and maintenance requirements
The exact information required depends on whether the project involves SIL assessment, SIL verification, SIS evaluation, LOPA, or broader lifecycle support.
Typical Deliverables
Depending on the project scope, deliverables may include:
- LOPA worksheets
- SIL assessment report
- SIL determination results
- SIF register
- SIL verification calculations
- PFDavg assessment
- SIS architecture review
- SIF performance evaluation
- Functional safety recommendations
- Proof-test considerations
- Action and recommendation registers
- Functional safety study report
Deliverables are tailored to the agreed scope and project requirements.
When Are Functional Safety Studies Required?
Functional safety activities may be relevant during different stages of a project, including:
New Projects
Functional safety requirements can be established during design to ensure that required instrumented protection is considered before systems are implemented.
Process Modifications
Changes to process conditions, equipment, control systems, or operating envelopes may require review of existing safety functions.
Existing Facilities
Existing SIS/SIF arrangements can be evaluated to identify gaps between required and achieved performance.
Safety System Upgrades
Functional safety assessment can support modifications to sensors, logic solvers, final elements, or SIS architecture.
Periodic Review
Functional safety is a lifecycle activity. Changes in process conditions, equipment, procedures, failure data, testing practices, or safety requirements may require reassessment.
Functional Safety Standards
Functional safety activities are commonly performed with reference to internationally recognized standards, including:
IEC 61508
IEC 61508 provides a generic framework for the functional safety of electrical, electronic, and programmable electronic safety-related systems.
IEC 61511
IEC 61511 addresses the functional safety of safety instrumented systems for the process industry sector and provides a lifecycle-based framework for SIS application.
The applicable edition, industry requirements, project specifications, and regulatory expectations should be considered when defining the methodology for a specific project.
Industries We Serve
Functional safety principles can be applied across industries where instrumented protection systems are used to manage process or equipment risks.
Our service areas include:
- Oil & Gas
- Chemicals & Petrochemicals
- Pharmaceuticals
- Power & Energy
- Manufacturing
- FMCG
- Food & Beverages
- Automotive
- Other process and industrial facilities
Why Functional Safety Matters
Effective functional safety management helps organizations:
- Establish appropriate safety requirements
- Reduce risk associated with hazardous process scenarios
- Evaluate the reliability of safety instrumented functions
- Identify gaps in SIS architecture
- Support risk-based engineering decisions
- Improve consistency in safety-system design and verification
- Support lifecycle management of safety instrumented systems
- Document assumptions, requirements, calculations, and recommendations
Functional safety should be treated as an engineering lifecycle rather than as a one-time SIL calculation.
Why Choose INDSAFE for Functional Safety Services?
INDSAFE combines process understanding with functional safety and instrumentation considerations to evaluate safety functions in their operating context.
Our approach focuses on:
- Risk-based functional safety assessment
- Integration of process safety and instrumentation perspectives
- Structured LOPA and SIL assessment
- SIF and SIS evaluation
- SIL verification based on defined assumptions and component data
- Practical engineering recommendations
- Documentation suitable for project and lifecycle requirements
The scope and methodology are tailored to the specific facility, process, safety function, and project requirements.
Frequently Asked Questions
What are Functional Safety Services?
Functional safety services help organizations assess, specify, design, verify, and manage safety-related instrumented systems and functions that are intended to reduce process or equipment risk.
What is SIL assessment?
SIL assessment determines the required Safety Integrity Level for an applicable Safety Instrumented Function based on the risk associated with a hazardous scenario and the required risk reduction.
What is SIL verification?
SIL verification evaluates whether the designed SIF can achieve its required SIL based on factors such as component reliability, architecture, diagnostics, proof testing, and other relevant parameters.
What is the difference between SIL assessment and SIL verification?
SIL assessment determines the required integrity level of a safety function.
SIL verification checks whether the proposed or implemented SIF design can achieve that required level.
They address different stages of the functional safety process.
What is LOPA?
LOPA, or Layers of Protection Analysis, is a structured semi-quantitative risk assessment technique used to evaluate specific hazardous scenarios and the effectiveness of independent protection layers.
Does LOPA determine SIL?
LOPA can support SIL determination when a Safety Instrumented Function is identified as an independent protection layer requiring a defined amount of risk reduction. The exact methodology depends on the project and applicable requirements.
Is LOPA the same as SIL assessment?
No. LOPA evaluates a hazardous scenario and its independent protection layers. SIL assessment determines the required integrity of an applicable safety instrumented function.
What is an SIS?
A Safety Instrumented System is a system designed to implement one or more Safety Instrumented Functions. It typically includes sensors, a logic solver, and final elements.
What is a SIF?
A Safety Instrumented Function is a specific safety function designed to detect a hazardous condition and initiate a defined action to reduce risk.
Which standards are used for functional safety?
IEC 61508 provides a generic functional safety framework, while IEC 61511 specifically addresses safety instrumented systems in the process industry sector. The applicable requirements depend on the project and industry context.
When should SIL verification be performed?
SIL verification is generally performed after the required SIL has been established and sufficient information about the SIF design and components is available. It may be revisited when the design, component data, testing arrangements, or other relevant assumptions change.
Technical References
Functional safety methodologies should be selected according to the application, project scope, and applicable standards.
Key references include:
- IEC 61508 – Functional safety of electrical/electronic/programmable electronic safety-related systems
- IEC 61511 – Functional safety: Safety instrumented systems for the process industry sector
- IEC 61882 – Hazard and operability studies (HAZOP studies) – Application guide
- Recognized process safety and functional safety guidance applicable to the specific project
Related Process Safety Services
Functional safety is closely connected with broader process safety, hazard identification, risk assessment, and compliance activities. Depending on the facility, project stage, and assessment scope, these studies may provide important inputs or complementary risk information.
Explore INDSAFE’s related services:
- Process Safety Management – structured systems and practices for managing process safety risks throughout the facility lifecycle.
- HAZOP – systematic identification of process hazards, deviations, causes, consequences, and safeguards.
- Quantitative Risk Assessment – quantitative evaluation of hazardous scenarios, consequences, event frequencies, and risk.
- Process Safety Gap Assessment – identification of gaps between existing process safety practices and applicable requirements or good engineering practices.
- MSIHC Audit & Compliance Services – assessment and compliance support for facilities covered by applicable hazardous-chemical regulatory requirements.
- ATEX, HAC & Dust Explosion Safety – assessment of hazardous areas and explosion risks associated with flammable gases, vapours, liquids, and combustible dusts.
- Chemical Reaction Hazard Assessment – evaluation of reactive chemical hazards, including runaway reactions, thermal decomposition, incompatibility, and pressure-generating reactions.
Get in Touch
Looking for functional safety services for SIL assessment, SIL verification, LOPA, SIS evaluation, or related functional safety activities?
Contact INDSAFE to discuss your facility, safety requirements, project stage, and scope of work.
Talk to our functional safety team to discuss your requirements.